Disable Firewall Ubuntu Server

Welcome to the wonderfully rebellious world of server tweaking! Disabling the firewall on your Ubuntu server might sound like a reckless act, but it’s actually a fantastic lea...
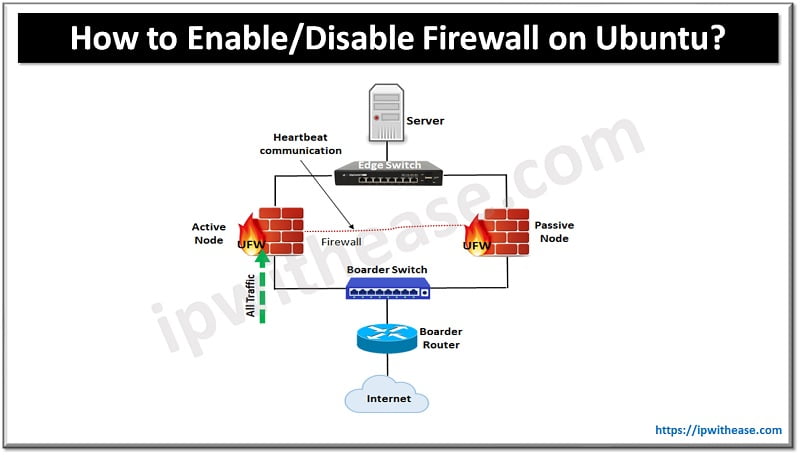
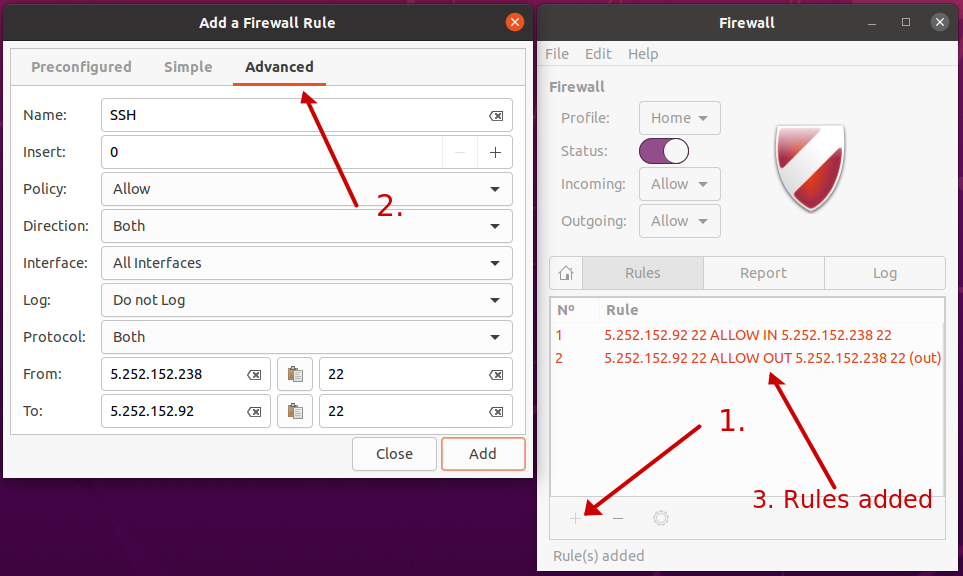
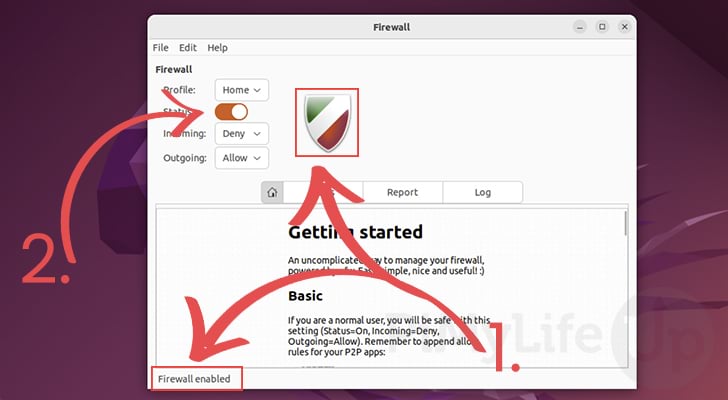
Welcome to the wonderfully rebellious world of server tweaking! Disabling the firewall on your Ubuntu server might sound like a reckless act, but it’s actually a fantastic learning tool and a necessary step in specific scenarios. Think of it as temporarily taking off the training wheels: you get to see the raw, unfiltered network traffic and understand exactly what your server is doing. The purpose here isn’t to leave it naked forever, but to diagnose connection issues, test new applications, or set up a custom firewall from scratch without old rules getting in the way. The advantage? Total control and a crystal-clear view of your server’s behavior.
Why would anyone want to do this? Imagine you’ve just installed a shiny new web server, but it’s refusing connections. You’ve double-checked the config, but nothing works. By temporarily disabling the firewall (usually UFW or iptables), you instantly know if the firewall is the culprit. It’s like pulling the brakes off a car to see if the engine actually runs—it’s a quick, satisfying diagnostic. Or, if you’re building a tight security setup from scratch, starting with a clean slate—no firewall at all—lets you add rules one by one, avoiding hidden legacy rules that might accidentally block critical services.
Here’s the creative part: you can turn this into a fun network detective game. After disabling the firewall, run a command like sudo ufw disable and then use netstat -tulpn to see every single open port. It’s like unlocking a secret map of your server’s soul! You’ll spot services you forgot were running—maybe an old FTP server or a test database. This hands-on exploration is invaluable for learning how ports and protocols interact. Plus, you can simulate attacks (safely, on a local network) to see how your applications behave without interference—a fantastic way to understand defense in depth.
Must Read
Practical tip: Never do this on a production server exposed to the internet unless you enjoy being hacked! Instead, use a clone or a virtual machine in your local lab. The command is simple: sudo ufw disable for UFW, or sudo iptables -F to flush iptables rules. To re-enable, just type sudo ufw enable. Keep a note of your original rules—maybe sudo ufw status numbered before disabling—so you can restore them instantly. It’s a power move, but with great power comes great responsibility.
Remember, disabling the firewall is not the end game, but a stepping stone. Once you’ve finished your testing, always re-enable it. For extra safety, set a cron job that re-enables the firewall every 10 minutes—just in case you get distracted and leave it open. This way, you can experiment freely while maintaining a safety net. In the end, you’ll gain a deeper respect for both the firewall and the raw power of an unprotected system—and that knowledge is the real treasure.