Nist 800 53 Vs Nist 800 171

Welcome to the surprisingly fun world of cybersecurity frameworks! Think of NIST 800-53 and NIST 800-171 not as dusty government manuals, but as your blueprint for building a...
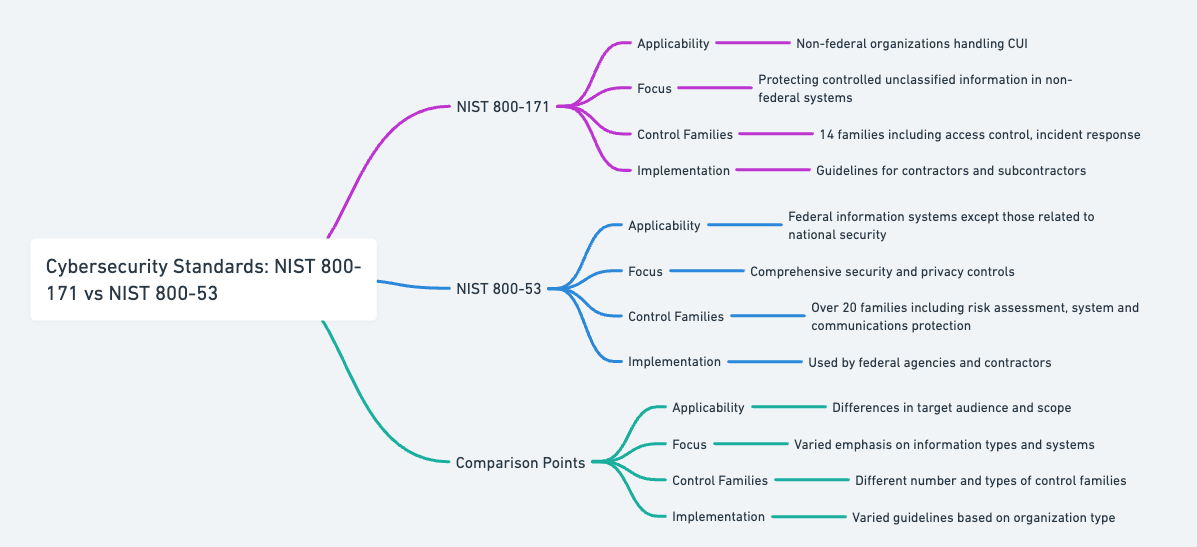
Welcome to the surprisingly fun world of cybersecurity frameworks! Think of NIST 800-53 and NIST 800-171 not as dusty government manuals, but as your blueprint for building a digital fortress. Understanding them helps you protect sensitive data, avoid fines, and even win more contracts. The best part? Once you know the difference, you can pick the right shield for your quest.
Here’s the simple distinction: NIST 800-53 is the full toolkit for federal agencies, packed with over a thousand controls for every risk imaginable. NIST 800-171 is its travel-sized cousin, designed specifically to protect Controlled Unclassified Information (CUI) in non-federal systems, like your small business or university. Think of 800-53 as the security for a spy agency, while 800-171 is the practical lockbox for a contractor handling secret research.
Imagine you’re a baker with a secret cookie recipe (your CUI). NIST 800-171 would require you to lock the recipe in a drawer, limit who has the key, and log every time someone opens it. That’s 110 simple, focused controls. Now, if you were running a national bakery chain (a federal agency), NIST 800-53 would demand a full security team, biometric locks, and an emergency plan in case a rival steals your dough—over 1,000 controls in total!
Must Read
For a creative twist, think of 800-171 as your startup’s security starter pack. You can implement its 14 control families (like Access Control and Awareness Training) with free tools: use multi-factor authentication for logins, encrypt your external hard drives, and train your team to spot phishing emails. It’s practical, cost-effective, and often required by Department of Defense contracts.
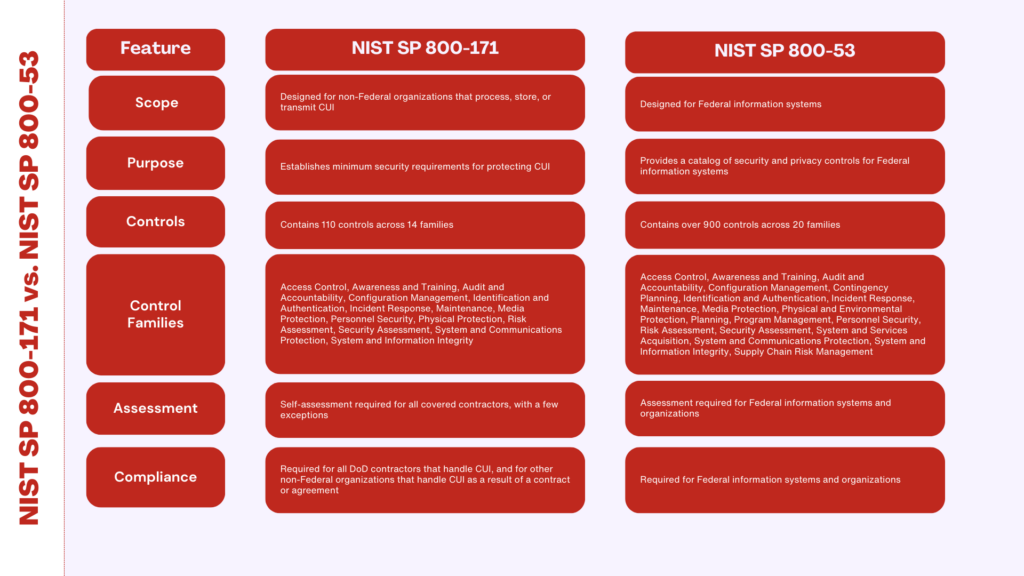 Essential Differences: NIST SP 800-171 and NIST SP 800-53 Explained
Here’s practical advice if you want to try it: Start with a gap assessment. Download the 800-171 checklist and compare it to your current practices. Use NIST’s free “Small Business Cybersecurity” guide to tackle the top 10 controls first. Don’t panic about perfection—focus on the core areas: identify who touches your CUI, limit access, audit activity, and maintain backups. That’s 80% of the battle.
Finally, remember that 800-171 is not a one-time thing. It’s a living process of continuous monitoring. Set a calendar reminder each month to review your access logs and update passwords. The payoff? You not only avoid penalties but build trust with partners who see you take data security seriously. So, pick your framework wisely: the full banquet (800-53) for big agencies, or the practical power meal (800-171) for everyone else. Now go lock that cookie recipe!

