Security + Objectives

So, you want to crack the Security+ exam, huh? You’ve heard it’s the golden ticket to a job where you get to yell “I told you so” when someone clicks a phishing link. But firs...

So, you want to crack the Security+ exam, huh? You’ve heard it’s the golden ticket to a job where you get to yell “I told you so” when someone clicks a phishing link. But first, you need to survive the objectives, which sound about as fun as a dental exam on a Monday.
Let’s be real—the CompTIA Security+ objectives are a beast. They cover everything from ransomware to zero-day exploits, and the official list is longer than the receipt at a five-star restaurant. But here’s the kicker: you don’t need to memorize every single one like a crazy parrot. You just need to think like a paranoid security guard at a rock concert.
Domain 1: General Security Concepts (The “Why Should I Care?” Part)
This is where you learn about Confidentiality, Integrity, and Availability—the CIA of cybersecurity. No, not that CIA. These three are the holy trinity that keeps your cat photos safe from hackers. If you lose one, your boss will cry, and you’ll be blamed for the “Great Corporate Panic of 2024.”
Must Read
Surprising fact: the first computer virus was actually a practical joke in 1971. It just said “I’m the creeper, catch me if you can!” Today’s viruses will steal your kidney, your Netflix password, and your will to live. So yeah, the stakes have changed.
Domain 2: Threats, Vulnerabilities, and Mitigations (The “Everything is Trying to Kill You” Part)
Imagine your network is a house, and hackers are raccoons with lockpicks. This domain teaches you about malware, social engineering, and phishing—the tools of the dark trade. Did you know that 91% of cyberattacks start with a phishing email? That’s like offering a burglar the keys to your front door because you thought they were a pizza delivery guy.
There’s also ransomware, which is basically a digital kidnapper for your files. If you ever get a pop-up that says “Pay me $500 in Bitcoin,” don’t panic. Just remember: you should have backed up your stuff. And maybe don’t name your computer “John-Wick.”
 CIA as Security Objectives V2 by Wentz Wu, ISSAP, ISSEP, ISSMP CISSP
Domain 3: Architecture and Design (The “Where Do You Put the Firewall?” Part)
This is where you get to talk about security zones and DMZs. No, not the Korean border—a DMZ is a demilitarized zone where your public servers hang out, practically naked. It’s like putting the weird uncle in the back room during Thanksgiving dinner: contained, but still dangerous.
You’ll also learn about cloud security, which is basically trusting someone else’s computer with your data. Fun fact: if you store your secrets in the cloud, you’re just renting a locker in a gym full of hackers. So encrypt everything, or cry later.
Domain 4: Implementation (The “Let’s Actually Do Stuff” Part)
This is the part where you pretend you know how to configure a firewall. You’ll use ACLs (Access Control Lists), which are like bouncers at a club: they let the cool IPs in and kick out the drunk ones. Also, you’ll learn about PKI—Public Key Infrastructure—which sounds fancy but is just digital handshakes. “Hey, are you really a bank? Prove it with a certificate.”
And here’s a hilarious reality: many companies still use passwords like “password123” or “admin.” So if you pass Security+, you become the person who gets to shame them. Lucky you.
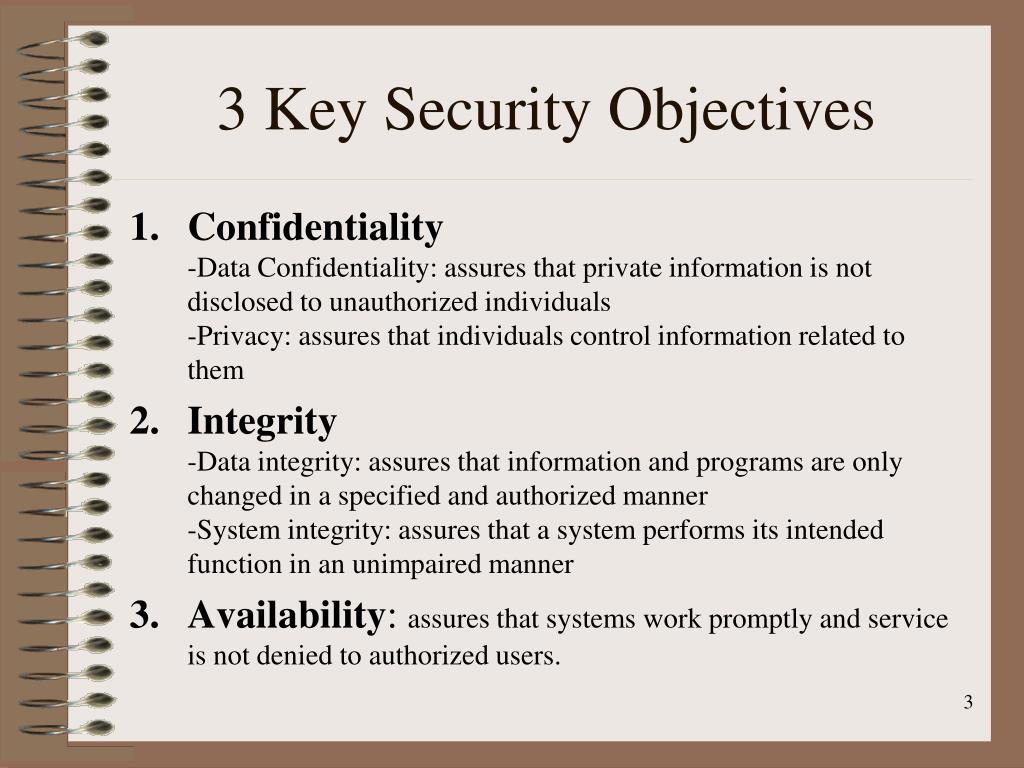 PPT - Chapter 18: Computer and Network Security Threats PowerPoint
Domain 5: Operations and Incident Response (The “Oh Crap, Now What?” Part)
When a breach happens, you don’t just scream and run. You follow the Incident Response Plan: identify, contain, eradicate, recover. It’s like the Heimlich maneuver for your network. If you do it right, you save the company. If you do it wrong, you end up in HR’s office.
Oh, and you’ll learn forensics. That’s where you dig through logs like an archaeologist with a bad attitude. Pro tip: never delete those logs. They’re your alibi when the boss asks, “Who gave the intern admin access?!”
Domain 6: Governance, Risk, and Compliance (The “Don’t Go to Jail” Part)
Last but least fun: risk management and laws. You’ll learn about GDPR, HIPAA, and PCI-DSS—acronyms that make you sound like a robot. The joke is that if you ignore compliance, the government will fine you more than your company is worth. So, respect the rules.
Here’s the bottom line: Security+ is your passport to a job where you get to be a digital superhero. But the exam? It’s like a game of chess with a octopus—confusing, but you’ll survive if you study smart and laugh at the chaos. Now go read those objectives. The hackers aren’t taking a coffee break.
