What Protocol Should Be Disabled To Help Mitigate Vlan Attacks

Welcome, network explorers! If you’ve ever felt like your VLAN setup is a fortress with a secret trapdoor, you’re right—and this article is the key to locking it. Taming VLAN...
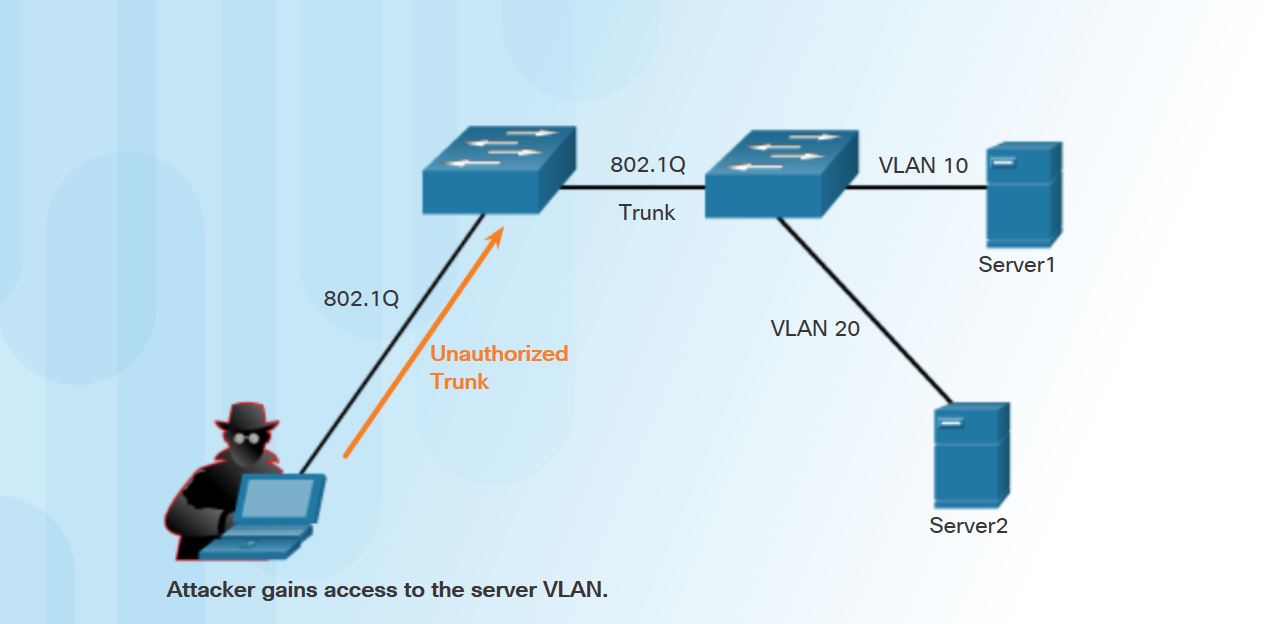
Welcome, network explorers! If you’ve ever felt like your VLAN setup is a fortress with a secret trapdoor, you’re right—and this article is the key to locking it. Taming VLAN attacks is actually fun once you realize that one simple, misunderstood protocol is often the culprit. Disabling it not only protects your data but also makes your network run leaner and meaner—like a sports car with no unnecessary weight. The best part? You don’t need to be a wizard; just a little know-how can save you from a world of headaches.
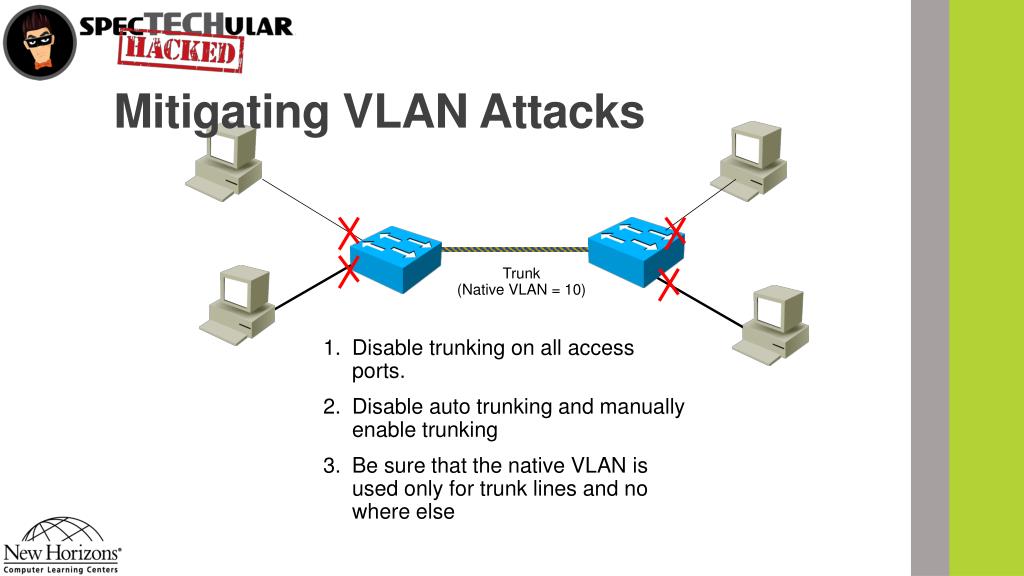
The protocol we’re talking about is Dynamic Trunking Protocol (DTP). Its purpose sounds friendly: “Let me negotiate a trunk for you!” But in reality, DTP is a security hazard waiting to happen. If an attacker connects a rogue switch, DTP can automatically form a trunk link, giving them access to all your VLANs. By disabling DTP on all end-user ports, you remove that automated welcome mat. Advantages? You get strict control over who trunks and who doesn’t—and zero-risk of VLAN hopping via “negotiation trickery.”
Let’s paint a creative picture: Imagine a party where DTP is the overly friendly bouncer who lets anyone with a fake ID into the VIP room. Without DTP, you’re clamping that door shut. For example, on a Cisco switch, you simply set unused ports to access mode and disable DTP with switchport mode access plus switchport nonegotiate. Suddenly, the attacker’s cable becomes harmless—like connecting a toy train to a highway. Another clever tactic: combine this with port security to limit MAC addresses per port. Now even if someone plugs in, they can’t spoof a trunk.
Must Read
Here’s a real-world tip: Always disable DTP on all user-facing ports—desktops, printers, security cameras. Even better, use a script to audit your switch configs for any port still running dynamic desirable or dynamic auto. And if you’re paranoid (in a good way), set unused ports to shutdown status. That way, they’re dark, cold, and unresponsive. Think of it as locking your car doors, removing the ignition key, and then parking it in a garage with a laser grid.
A second dangerous protocol to disable is VLAN Trunking Protocol (VTP) unless you absolutely need it. VTP syncs VLAN databases across switches, but a single corrupt update can erase your entire VLAN config. The advice? Set VTP to transparent mode on all switches—you still manage VLANs locally, but the “sync bomb” risk vanishes. For extra safety, use vtp mode transparent and no vtp password (since passwords only slow down, not stop, malicious changes).
 What Protocol Should Be Disabled to Help Mitigate VLAN Attacks?
Ready to start? Pick one switch, log in, and type show interfaces trunk to see what’s currently trunking. If you spot a port that shouldn’t be a trunk, shut it down immediately. Then, for every access port, run: switchport mode access and switchport nonegotiate. You’ll feel like a digital locksmith who just patched all the skeleton keys. Practice this on a lab switch first—small steps, big safety. The immediate reward is peace of mind, knowing your VLANs are no longer whistling open.
In summary, disabling DTP and VTP (or relegating VTP to transparent mode) is the simplest, most cost-effective way to slash VLAN attack surfaces. You gain complete control, stop automated trunk negotiations, and prevent database disasters. It’s like giving your network a pair of goals: secure and simple. So go ahead, log in, and turn off those chatty protocols—your inner network superhero will thank you!